‘If you target the American people, justice will find you,’ FBI chief Kash Patel warns cybercriminals
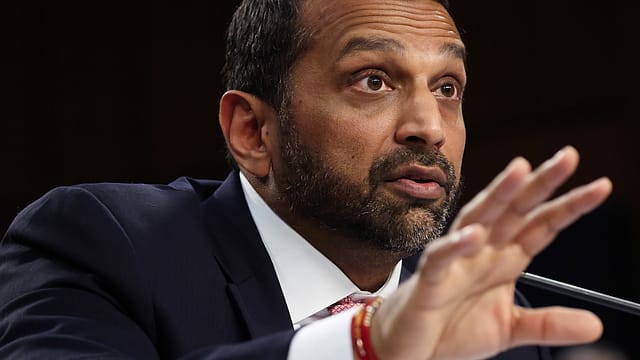
FBI Director Kash Patel warned cybercriminals targeting Americans that the agency would pursue them around the world. In a post on X on Friday, November 20, Patel said the FBI was taking a more aggressive approach under President Donald Trump through Operation Winter Shield, an effort to prevent attacks on businesses and public institutions and strengthen US cyber defences.
“Through Operation Winter Shield, we’re going on offence against cyber threats, strengthening our nation’s defences, and working with our partners to protect American businesses, government systems, and critical infrastructure,” Patel wrote.
“Our message is simple: If you target the American people, justice will find you,” he added.
Patel’s warning followed two developments on Thursday. The White House named an acting director to oversee national cybersecurity policy, and JPMorgan Chase disclosed that attackers had gained access to marketing data held by companies that provide services to the bank. The bank said the breach was separate from a disruption some customers had experienced earlier in the week.
The Wealth Issue 2026
06 Nov 2026 - Vol 05 | Issue 45
Portraits of Dreamers and Doers under 35
Kirsten Davies takes over as acting national cyber director
The White House named Kirsten A. Davies acting head of the Office of the National Cyber Director, succeeding Sean Cairncross. The permanent appointment requires Senate confirmation. Cairncross had overseen federal cybersecurity policy and strategy since August 2025.
In a statement on Thursday night, Cairncross said it had been an “honour of a lifetime to serve” under Trump. Davies thanked the president and senior administration officials in a post on X and outlined her priorities for protecting the country’s digital infrastructure.
US Secretary of State Marco Rubio welcomed the appointment. “Congratulations to the new National Cyber Director Kirsten Davies. Look forward to working together to strengthen America’s cybersecurity,” he wrote.
What the JPMorgan vendor breach may have exposed
The cyberattack on JPMorgan’s third-party providers potentially exposed personal information belonging to about 16,000 wealthy customers. Fox News reported that a ransomware group calling itself n0n had claimed responsibility for leaking the records. The information reportedly included email addresses, phone numbers and account IDs. Business partners associated with Visa and Mastercard were also affected, according to the report.
The JPMorgan records appeared to be linked to its Reserve programme, an invitation-only Visa credit card generally available to clients with more than $10 million in assets under management. The bank’s own account was narrower than the reported list of exposed details. Its investigation had identified marketing data at outside vendors as the material the attackers accessed.
“We have learned that third parties who provide services to the firm were the target of a cyberattack. Based on our investigation so far, we believe the attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses,” JPMorgan said on X.
Visa traced the breach to a vendor in the Asia-Pacific region. JPMorgan, Visa and Mastercard said the attack had spared their core payment networks and that card numbers remained secure. JPMorgan said it would contact affected customers directly where appropriate and offer support, including free credit monitoring.
A software bug caused the earlier banking disruption
Customers had also encountered trouble processing transactions at JPMorgan and several other banks earlier in the week. A software bug caused those difficulties. According to an industry executive, the Office of the Comptroller of the Currency made inquiries to establish how customers had been affected and what the banks had told them.
“There is no connection to the service disruption some customers experienced earlier this week,” JPMorgan said in its statement on the vendor breach.
The distinction has become important after a series of disruptions across finance, technology and aviation. A nationwide Federal Aviation Administration ground stop interrupted US air travel last week. Microsoft experienced a global email outage, while cryptocurrency exchange Binance suffered a cyberattack last month. Separate reports said malware had been found on about 180 major websites.
Official accounts have largely ruled out cyberattacks as the cause of the aviation and email outages. For JPMorgan customers, the two incidents carried different consequences: the software fault affected transactions, while the attack on vendors may have exposed personal information even as banking services continued to operate.
With inputs from ANI